


Get
93% Off!
on Lifetime Exclusive Deal
Don’t Miss out this deal, it comes with Password Manager Free of cost.
A WiFi Pineapple is a device that can imitate wireless networks and help security professionals test how devices respond to rogue access points. In the wrong hands, the same technology can be used to monitor or manipulate wireless connections.
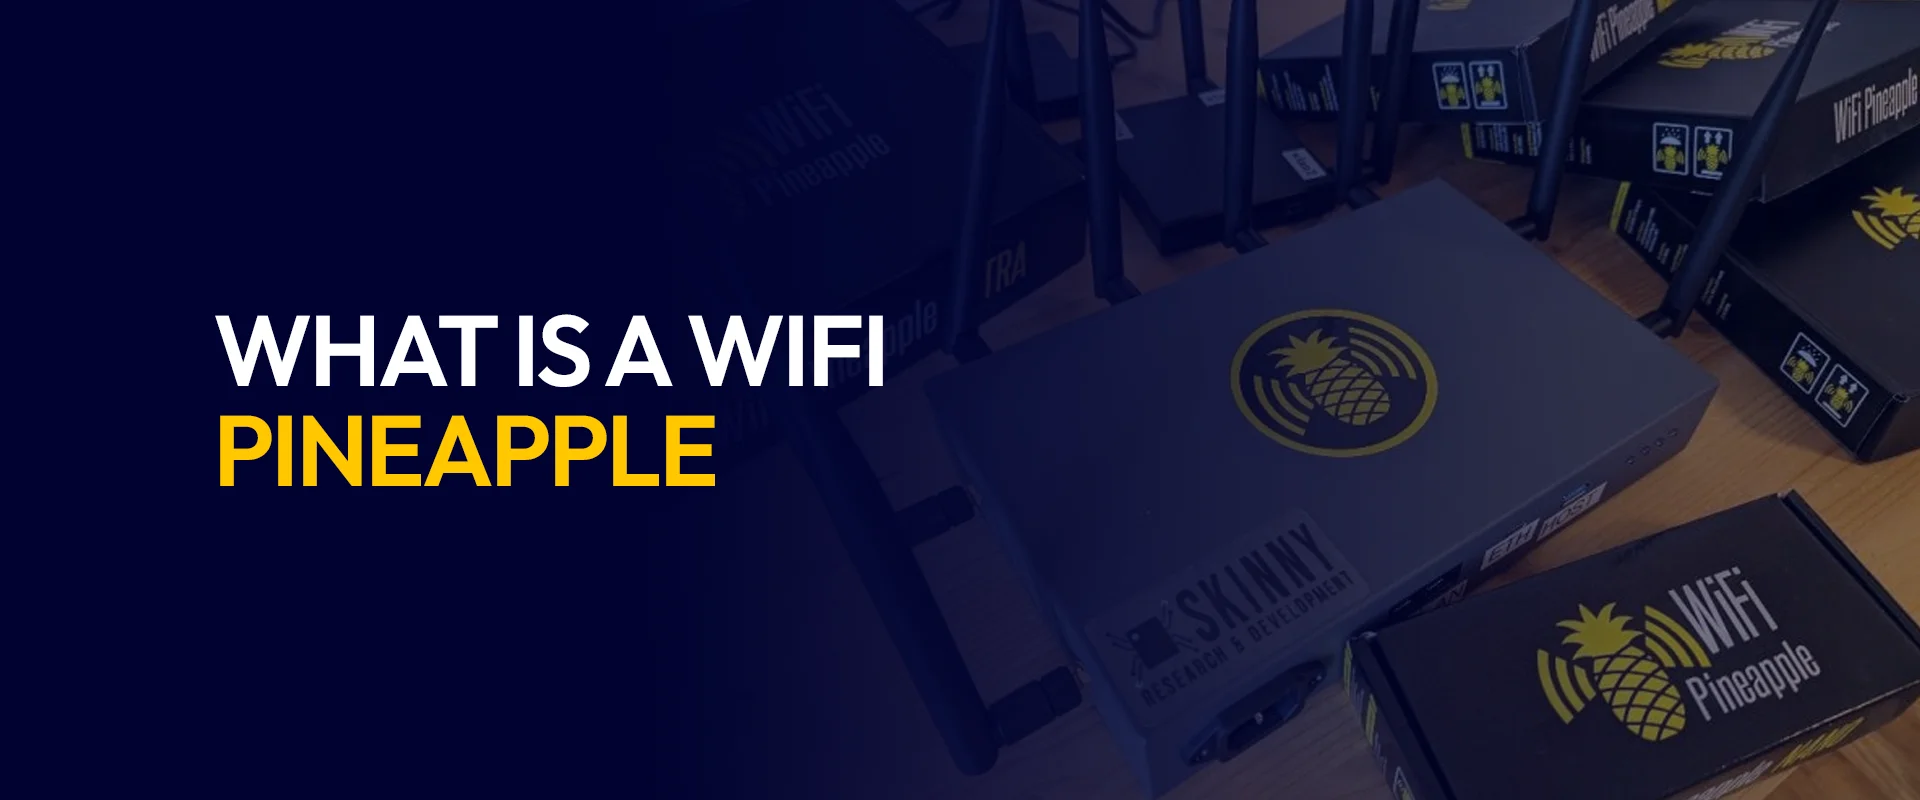
WiFi Pineapples are made by Hak5 and are designed primarily for WiFi penetration testing and security research. Hak5 describes its WiFi Pineapple products as platforms for testing wireless security, reconnaissance, and rogue access point attacks.
That makes the technology useful for authorized security testing. It also creates risks for people who connect to public WiFi without taking basic precautions.
So, what exactly is a WiFi Pineapple? How does it work? And can a VPN protect you from one? Let’s take a closer look.
A WiFi Pineapple is a portable wireless penetration-testing device made by Hak5.
It can analyze nearby wireless networks and simulate access points. Depending on the model and configuration, it can also be used for rogue access point testing, man-in-the-middle scenarios, deauthentication attacks, and wireless reconnaissance.
The device is built for legitimate security work. For example, a penetration tester may use it to check whether employees automatically connect to untrusted networks.
The problem starts when someone uses the same capabilities without permission.
A rogue access point can be made to look like a trusted WiFi network. If a device connects to it, the attacker may gain a position between the device and the internet. What they can actually see or manipulate depends on the network, device, encryption, and services being used.
This is why public WiFi security still matters.
You sit down at a coffee shop and connect to its WiFi. Your phone recognizes the network and joins it automatically. Everything seems normal. But what if that network is not the real one?
A WiFi Pineapple can take advantage of how devices search for and connect to wireless networks.
Here is a simplified look at how a typical rogue access point attack can work.
Your phone or laptop regularly looks for available wireless networks.
Devices may also remember networks they have used before. Depending on the device and settings, it may attempt to reconnect to a familiar network when it becomes available.
This behavior can create an opportunity for a rogue access point.
A WiFi Pineapple can be configured to imitate wireless networks.
For example, imagine that you previously connected to a network called “CoffeeShop_WiFi.”
A rogue access point could advertise a network using the same or a similar name.
If your device accepts the connection, it may associate with the attacker’s equipment instead of the legitimate access point.
This is commonly associated with an evil twin attack.
Once a device connects to a rogue access point, the attacker may be able to position that equipment between the device and the internet.
This is known as a man-in-the-middle position.
However, this does not mean that everything on the device automatically becomes visible.
Modern HTTPS connections encrypt application traffic. End-to-end encrypted apps can provide additional protection. A VPN can also create an encrypted tunnel between the device and a VPN server.
The exact exposure depends on what security protections are already in place.
Wireless attacks can also attempt to disconnect devices from legitimate access points.
Deauthentication attacks send management frames that can cause devices to disconnect from a WiFi network.
An attacker may then try to get those devices to connect to a rogue access point.
These techniques are commonly used in authorized wireless security testing. Using them against networks or devices without permission can create legal and security problems.
A WiFi Pineapple is not a single-purpose hacking tool. Its capabilities depend on the model, software, modules, and how it is configured.
Some commonly associated attack techniques include the following.
An evil twin is a fake wireless access point that imitates a legitimate network.
For example, a hotel might have an SSID called “Hotel_Guest.” An attacker could create a rogue network using the same or a very similar name.
A device may connect to the wrong network if it does not properly verify the access point.
Rogue networks can also be used with fake captive portals.
A user might connect to WiFi and see a page asking for an email address, password, or other information before granting internet access.
If that page is controlled by an attacker, anything entered into it could be collected.
This is especially concerning in places where captive portals are normal, such as hotels, airports, cafes, and conference centers.
DNS translates domain names into IP addresses.
If an attacker can manipulate DNS traffic, they may attempt to redirect a user to a different website.
This can be used as part of a phishing attack. A fake page may look similar to a legitimate service and attempt to convince the victim to enter sensitive information.
Attackers may also attempt to obtain session information from poorly protected connections.
Modern HTTPS and secure application design make many older session-hijacking techniques more difficult. Still, using untrusted networks without additional protection can increase your exposure.
A rogue access point may provide an opportunity to manipulate certain traffic that is not adequately protected.
This can include attempts to redirect connections, inject content, or interfere with network communication.
Again, encryption matters. Properly encrypted traffic is much harder for an attacker on the local network to read or modify.
Wireless security tools can also be used to test network resilience.
For example, deauthentication traffic can repeatedly disconnect devices from a wireless network.
In an authorized penetration test, this can help an organization understand its wireless security weaknesses.
Outside an authorized test, deliberately disrupting another person’s network can be illegal and harmful.
WiFi Pineapple attacks are most relevant when you use public or unfamiliar wireless networks.
Common locations include:
The risk is higher when your device automatically joins saved networks.
You may think you are choosing a WiFi network manually. In reality, your phone or laptop may already have connected based on its saved network settings.
That is why automatic connection settings deserve attention.
Owning a WiFi Pineapple is not the same as using it against other people.
Hak5 markets its wireless security tools for authorized penetration testing and security research. Security professionals can use them to identify weaknesses in wireless networks.
Using a device to intercept, disrupt, or access someone else’s communications without permission can violate laws and regulations.
The exact rules depend on where you live and what actions are performed.
If you use wireless security equipment for testing, make sure you have clear authorization and stay within the agreed scope of the test.
You do not need advanced networking knowledge to reduce the risk.
A few simple changes can make a significant difference.
A VPN is one of the most useful tools for protecting your traffic on an untrusted network.
A VPN creates an encrypted connection between your device and a VPN server. When the VPN tunnel is active, someone operating the local WiFi network should not be able to read the contents of the protected traffic.
This is useful if you accidentally connect to a rogue access point.
For example, if your laptop connects to a fake cafe network, a properly configured VPN can prevent the network operator from simply reading the contents of your VPN-protected traffic.
A VPN does not make a rogue network disappear. It also cannot protect information that you voluntarily enter into a malicious fake website or captive portal before the VPN connection is established.
For that reason, use a VPN together with other security habits.
Check your device’s WiFi settings and disable automatic joining for networks you do not trust.
On iPhone, you can manage Auto-Join settings for individual networks.
Android settings vary between manufacturers, but similar controls are available on many devices.
This reduces the chance of your device automatically joining a suspicious network.
Once you leave a hotel, airport, cafe, or other public location, consider removing that WiFi network from your saved networks.
The fewer unnecessary public networks your device remembers, the fewer networks it may try to reconnect to later.
Always check that websites use HTTPS, especially when entering passwords, payment information, or other sensitive data.
HTTPS does not protect against every type of rogue WiFi attack. However, it encrypts communication between your browser and the website when properly implemented.
Modern browsers also warn users about many insecure connections.
If you are connecting to WiFi at a hotel, airport, cafe, or event, ask staff for the exact network name.
Do not assume that the strongest-looking signal is the legitimate one.
Be careful with networks that have similar names, unusual spellings, or unexpected login pages.
A WiFi Pineapple and a VPN have completely different purposes.
A WiFi Pineapple is a wireless security testing platform. It can be used by authorized professionals to identify weaknesses in WiFi networks.
A VPN is a privacy and security tool that encrypts traffic between your device and a VPN server.
The two technologies can interact in an attack scenario.
For example, your device could connect to a rogue WiFi network. If your VPN is already active and working correctly, the attacker controlling that network has a much harder time reading the contents of your VPN-protected traffic.
This is one reason a VPN is useful when using public WiFi.
FastestVPN can add an important layer of protection when you use public or unfamiliar WiFi.
Its VPN connection encrypts traffic between your device and the VPN server. FastestVPN also offers features such as a kill switch, DNS leak prevention, multiple VPN protocols, and WiFi security.
The kill switch is particularly useful if your VPN connection unexpectedly drops. It can prevent your device from continuing to access the internet outside the VPN connection, depending on your settings and platform.
FastestVPN supports devices including Windows, macOS, iOS, Android, and other platforms.
Still, a VPN is not a complete replacement for safe browsing.
You should combine it with automatic WiFi controls, HTTPS, strong passwords, multi-factor authentication, and careful network selection.
The safest approach is to connect to a trusted network, enable your VPN, and then start using sensitive websites or apps.
A WiFi Pineapple is a wireless penetration-testing device developed by Hak5. It can be used to assess WiFi security, simulate rogue access points, perform wireless reconnaissance, and test how devices respond to different network attacks.
A WiFi Pineapple can imitate wireless networks and act as a rogue access point. If a device connects to it, the operator may be able to observe or manipulate certain network traffic, depending on the security protections being used.
The device itself is a security-testing tool. Using it without authorization to intercept communications, access systems, or disrupt networks can violate laws. Always have permission before conducting wireless security testing.
A VPN can protect the contents of traffic that passes through its active encrypted tunnel. This can make intercepted VPN traffic unreadable to someone controlling the local WiFi network. A VPN does not prevent your device from connecting to a rogue network.
An evil twin attack uses a fake WiFi access point that imitates a legitimate network. If a device connects to the fake network, the attacker may gain a position to monitor or manipulate certain traffic.
Disable automatic joining for unnecessary WiFi networks, forget old public networks, verify network names before connecting, and use a VPN on networks you do not fully trust.
It can be used as part of attacks designed to collect credentials, such as fake login pages. However, it does not automatically reveal every password or encrypted connection simply because a device connects to it.
Hak5 currently sells several WiFi Pineapple models and related products. Pricing varies by model and configuration, so check the manufacturer’s current product listings for the latest price.
A WiFi Pineapple shows why you should not automatically trust public WiFi.
The technology has legitimate uses. Security teams can use it to test wireless networks and identify weaknesses before criminals exploit them.
For everyday users, the important lesson is simple.
Do not let your device automatically connect to every saved network. Verify public WiFi before using it. Look for HTTPS. And use a trusted VPN when connecting through networks you do not control.
These steps will not make you invisible online. But they can significantly reduce what someone operating a rogue WiFi network can learn about your activity.
Take Control of Your Privacy Today! Unblock websites, access streaming platforms, and bypass ISP monitoring.
Get FastestVPN
© Copyright 2026 Fastest VPN - All Rights Reserved.
Don’t Miss out this deal, it comes with Password Manager Free of cost.